
How to Remove a PowerShell ISE Snippet

The Snippet functionality in PowerShell is a really cool feature.  It allows you to easily add templates to the ISE to help speed up your coding.  Recently I added a new snippet and discovered that I messed up the description.  Well, looking at the commands provided to us from the ISE Module, we do not have much of a choice when it comes to modifying the description, or even removing the snippet from the ISE.
PS C:\> Get-Command -Module ISE

CommandType     Name                                               Version    Source                                             
-----------     ----                                               -------    ------                                             
Function        Get-IseSnippet                                     1.0.0.0    ISE                                                
Function        Import-IseSnippet                                  1.0.0.0    ISE                                                
Function        New-IseSnippet                                     1.0.0.0    ISE                                                


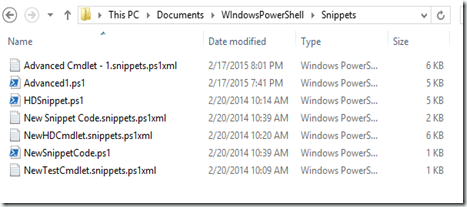
Well, here is how you fix that.  Simply browse to your Documents\WindowsPowerShell\Snippets folder.  Here you can see the file for my Advanced1 Snippet.  It is called Advanced Cmdlet – 1.snippets.ps1xml.
image
Simply delete this file and restart the ISE.  That is all that it takes.
In my situation, I just simply re-register the snippet with the correct description. Here is the code that I used to register the Snippet.
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18 
$Text = (Get-Content -Raw -Path "C:\Users\JASON\Documents\WIndowsPowerShell\Snippets\Advanced1.ps1")

$Desc1 = "Advanced Cmdlet Template"
$Desc2 = "`n--------------------------------------------------"
$Desc3 = "`n  Use when you need to be able to access remote"
$Desc4 = "`n  clients with PowerShell Remoting."
$Desc5 = "`n---------------------------------------------------"

$Props = @{
    "Title" = "Advanced Cmdlet - 1";
    "Description" = $Desc1+$Desc2+$Desc3+$Desc4+$Desc5
    "Author" = "Jason A. Yoder"
    "Text" = $Text
    "CaretOffset" = 10

}

New-IseSnippet @Props

And here is what my description looks like:
image

Comments

Popular posts from this blog

How to run GPResult on a remote client with PowerShell

In the past, to run the GPResult command, you would need to either physically visit this client, have the user do it, or use and RDP connection.  In all cases, this will disrupt the user.  First, you need PowerShell remoting enabled on the target machine.  You can do this via Group Policy . Open PowerShell and type this command. Invoke-Command –ScriptBlock {GPResult /r} –ComputerName <ComputerName> Replace <ComputerName> with the name of the target.  Remember, the target needs to be online and accessible to you.

Set up your Environment to utilize Invoke-GPUpdate

I’m sitting in O’Hare enjoying my 3 hour layover as I get ready to teach a Windows 10 class in Fort Wayne.  I’m actually prepping for my class in Fort Wayne in a few weeks, 10982 Supporting and Troubleshooting Windows 10.  This class is very much like the Windows 7 version that I used to teach so I decided to up the detail quite a bit.  In the GPO troubleshootin chapter, I’m including a demonstration on how to use PowerShell’s Invoke-GPUpdate.  I needed to make sure the environment is set up for me to be able to utilize this cmdlet.  If you read the Notes section on Invoke-GPUpdate’s help file, you will see there are three firwall rules that need to be in place:          Remote Scheduled Tasks Management (RPC)          Remote Scheduled Tasks Management (RPC-ERMAP)          Windows Management Instrumentation (WMI-IN) I decided to create a little PowerShell script to crea...

Where did a User’s Account Get Locked Out?

Updated: May 15, 2015 When this article was originally published, two extra carriage returns were add causing the code to malfunction.  The code below is correct.   My client for this week’s PowerShell class had a really interesting question. They needed to know where an account is being locked out at. OK, interesting. Apparently users hop around clients and forget to log off, leading to eventual lock out of their accounts. The accounts can be unlocked, but are then relocked after Active Directory replication. This problem is solved in two parts. The first one is to modify the event auditing on the network. The second part is resolved with PowerShell. The first part involves creating a group policy that will encompass your Domain Controllers. In this GPO, make these changes. Expand Computer Configuration \ Policies \ Windows Settings \ Security Settings \ Advanced Audit Policy Configuration \ Audit Policies \ Account Management Double click User Account Management C...